
06 June 2026 - 07:51
Category: IT Fail
Worms in the npm registry, how novel
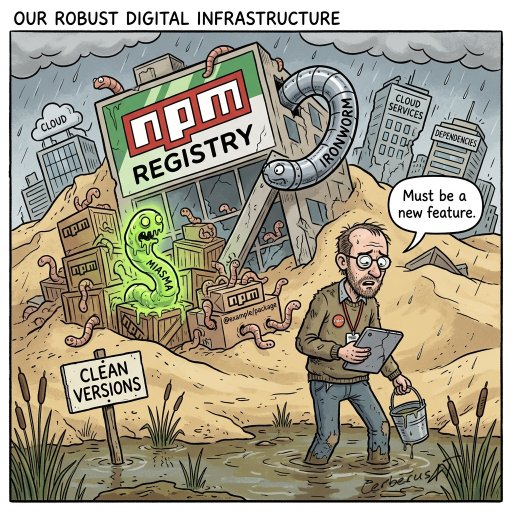
Threat actors poisoned over fifty npm packages with IronWorm and Miasma to distribute a Rust-based info-stealer. Who doesn't love their building blocks pre-loaded with malware?
Source: The Hacker News
The Full Story
Developers relying on the npm ecosystem get to deal with the joy of IronWorm and Miasma, two lovely worm variants currently piggybacking on over fifty poisoned packages. These malicious additions are designed to distribute a Rust-based information stealer, because standard software wasn't exciting enough. Trying to protect ourselves from this supply chain disaster feels like searching for clean water in a swamp, requiring us to somehow dodge these contaminated versions. It is just another day of realizing our entire digital infrastructure is built on sand.