
03 June 2026 - 12:43
Category: IT Fail
Web servers knocked out in seconds
The default HTTP/2 configuration of major web servers is vulnerable to a rapid offline exploit. Clearly, keeping a website online is far too much to ask these days.
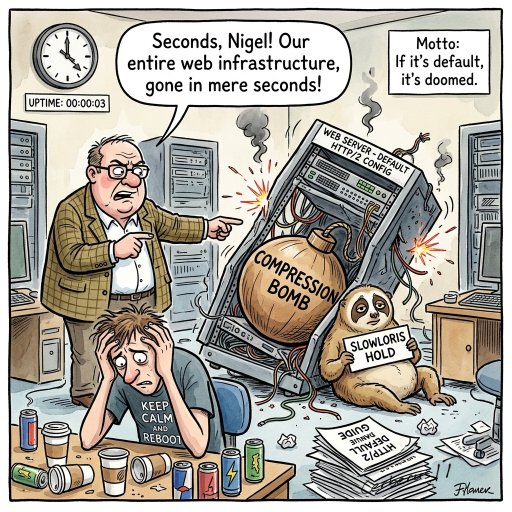
Source: SecurityWeek
The Full Story
A charming new exploit chain combining a compression bomb and a Slowloris-style hold can knock major web servers offline in mere seconds. This lovely threat targets anyone running the default HTTP/2 configuration, proving once again that default settings are a recipe for absolute disaster. Securing our networks against this rapid-fire shutdown requires sorting out this flawed default HTTP/2 configuration, assuming we can drag ourselves away from our endless despair long enough to do so.
#http2bomb
#offlineagain