
29 June 2026 - 07:51
Category: IT Fail
Trusting public packages is a mistake
Hijacked npm and Go packages are now deploying Python malware via VS Code tasks across every major operating system. Because trusting open-source repositories always ends so well.
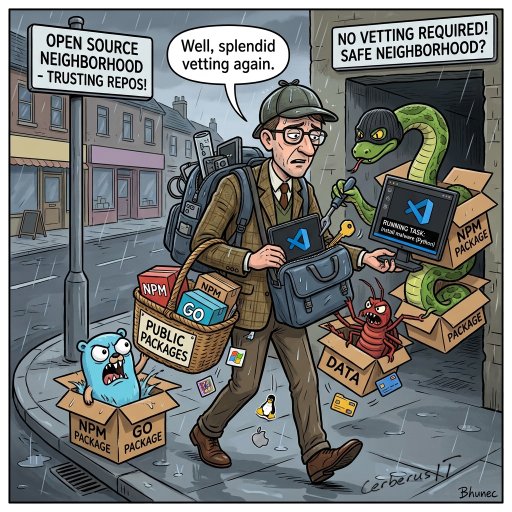
Source: The Hacker News
The Full Story
Our endless faith in open-source code has been rewarded yet again by hijacked npm and Go packages using VS Code tasks to drop a lovely Python infostealer. This wonderful surprise affected developers on Windows, Linux, and macOS who trusted these packages to do their jobs. We supposedly protect ourselves by actually vetting the npm and Go packages we download, rather than treating public repositories like a safe neighborhood where no one ever gets mugged.
#trustissues
#opensource