
30 April 2026 - 18:11
Category: Trust Issues
Sandworms in the SAP Supply Chain
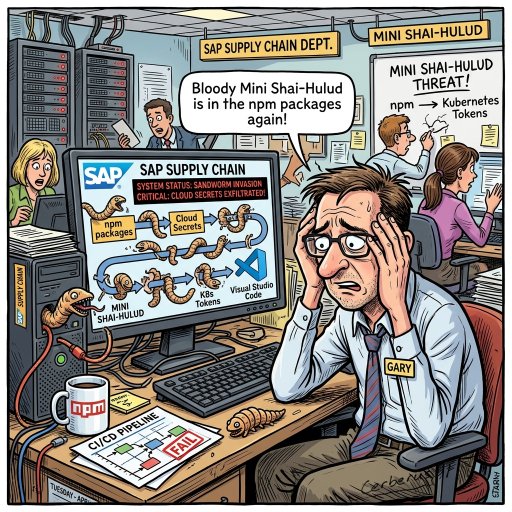
Poisoned SAP npm packages are currently siphoning cloud secrets and GitHub tokens your developers haven't leaked yet. It’s nice to know our tools are working against us.
Source: csoonline.com
The Full Story
A charming campaign named Mini Shai-Hulud has decided that SAP developers have it far too easy, poisoning npm packages to exfiltrate cloud secrets and Kubernetes tokens. This little stowaway even makes itself at home by modifying Visual Studio Code and Claude Code configurations to ensure it stays relevant every time a repository is opened. To avoid this particular headache, we might try verifying our dependencies before inviting them into our CI/CD pipelines like unwanted house guests. One day, we might actually trust a package manager, but that day certainly isn't a Tuesday in April.