23 October 2026 - 12:51
Category: IT Fail
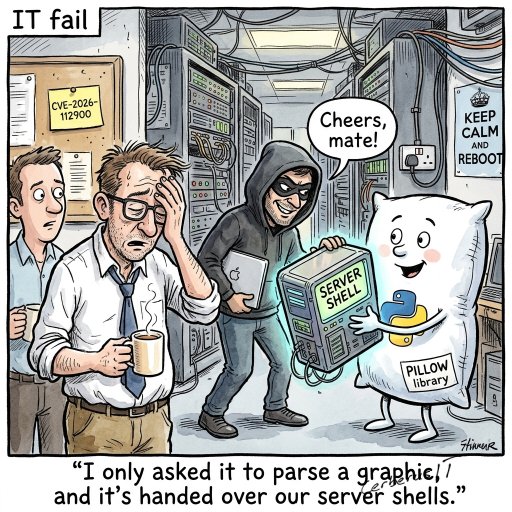
Python Pillow Hands Over Server Shells
Python's Pillow library runs arbitrary server commands simply by opening a specially crafted image file. Because viewing pictures was far too safe anyway.
Source: The Hacker News
The Full Story
Here we go again, with servers utilizing Python's beloved Pillow image library generously executing operating system commands if someone simply feeds it a crafted filename. Shielding our infrastructure demands stopping this library from being told to open malicious file names tied to CVE-2026-112900 before attackers take over. Why do we even bother parsing graphics when basic image libraries can surrender the entire operating system? Just another Tuesday where opening a file requires praying to the IT deities.
#pillowfail
#pythonwoes