
12 August 2026 - 12:17
Category: Trust Issues
PyPI Package Theft: Just Another Tuesday
Poisoned LiteLLM packages on PyPI quietly stole credentials from over 2,500 enterprises. Time for another joy-filled afternoon rotating every single secret key.
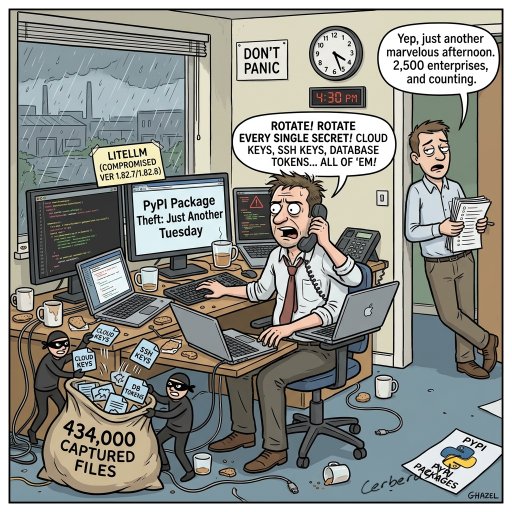
Source: The Hacker News
The Full Story
Some brilliant souls published compromised LiteLLM versions 1.82.7 and 1.82.8 on PyPI, helpfully harvesting cloud keys, SSH keys, and database tokens for bad actors. This lovely surprise ensnared over 2,500 enterprises and yielded a massive dataset of 434,000 captured files for researchers to sift through. Rather than waiting around for confirmation that our infrastructure has been plundered, victims are urged to immediately rotate all secrets and credentials without delay. Just another marvelous afternoon spent resetting every key in sight.