
01 October 2026 - 07:51
Category: IT Fail
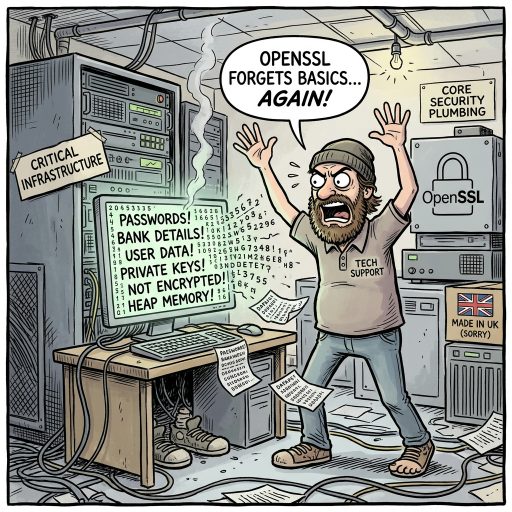
OpenSSL Forgets Encryption Basics Again
OpenSSL is graciously blabbing raw heap memory without any encryption. Truly reassuring performance from core security plumbing.
Source: The Hacker News
The Full Story
Here we go again with OpenSSL managing to leak sensitive unencrypted heap data or crash entirely just because a handshake message stalled. Anyone running DTLS gets the joy of discovering their core cryptographic library is basically a glorified sieve. The only way to stop remote endpoints from reading unencrypted memory is to deploy OpenSSL's latest updates without delay. We just love spending our evenings patching the very software that was meant to keep us safe.
#opensslfail
#heapleaks