
30 July 2026 - 07:34
Category: IT Fail
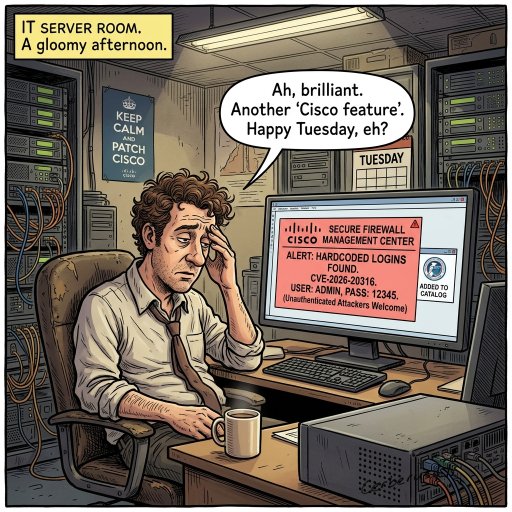
Hardcoded logins, just another Tuesday
CISA added a Cisco FMC zero-day to its list because someone thought hardcoded credentials were fine. Why bother setting passwords when vendors leave built-in ones anyway?
Source: The Hacker News
The Full Story
Here we go again with Cisco Secure Firewall Management Center software leaving static low-privilege credentials for unauthenticated attackers to snatch sensitive data. Naturally, this absurd CVE-2026-20316 flaw earned a spot on CISA's catalog because attackers love chaining it to elevate privileges. Protecting our poor infrastructure means installing Cisco patches to block these default credentials before someone chains them. Just another Tuesday in IT where vendor defaults ruin my afternoon.
#ciscofail
#sameoldit