
22 May 2026 - 18:02
Category: Trust Issues
CISA's brilliant contractor key leak
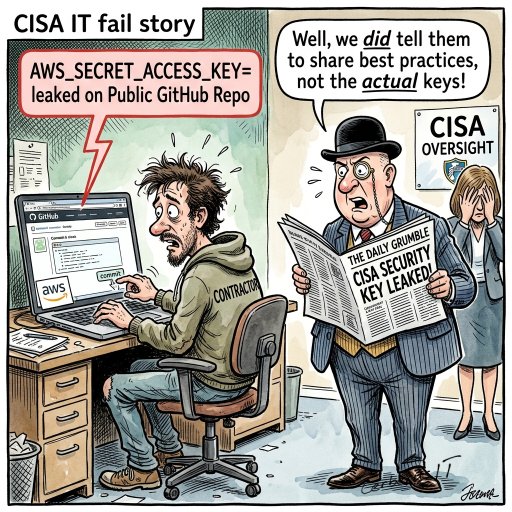
CISA is busy containing damage after a contractor posted AWS GovCloud keys on a public GitHub account. Good to see our security guardians leading by example.
Source: krebsonsecurity.com
The Full Story
Our cybersecurity guardians at CISA are currently learning the hard way that letting contractors publish sensitive AWS GovCloud keys on public GitHub accounts isn't a brilliant strategy. This unfortunate display of trust issues naturally affects the agency's already stellar security reputation and leaves US lawmakers pretending to be utterly shocked by basic human incompetence. If we wish to protect our own systems from such third-party helpfulness, we might start by actually monitoring what our contractors are doing with our secrets before they post them for the entire world to appreciate.