
15 July 2026 - 07:51
Category: Trust Issues
CISA leaves the front door open
Our cybersecurity overlords at CISA accidentally left their AWS GovCloud keys on a public GitHub for six months. I suppose keeping secrets is hard when you actually have to try.
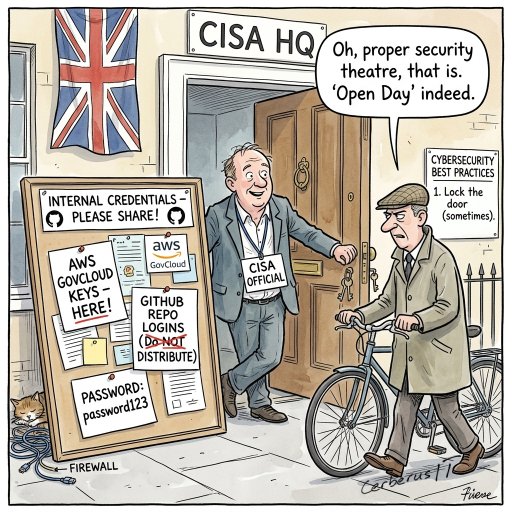
Source: TECHMANIACS.com
The Full Story
In a brilliant display of cybersecurity leadership, a third-party developer working with CISA kindly shared dozens of internal credentials, including AWS GovCloud keys, with the entire internet on GitHub. These sensitive keys spent half a year sitting in public view before anyone bothered to notice and revoke them, proving that security posture is mostly theatrical. If we hope to shield our own digital assets from this flavor of sheer incompetence, we must implement rigorous automated scanning of all public repositories. Alternatively, we could just accept that our data is destined to be public anyway.